How to Build a Password Routine You Can Maintain
A sustainable password routine combines unique passwords, a password manager you can use confidently, and recovery details kept current—without turning account security into a daily chore.
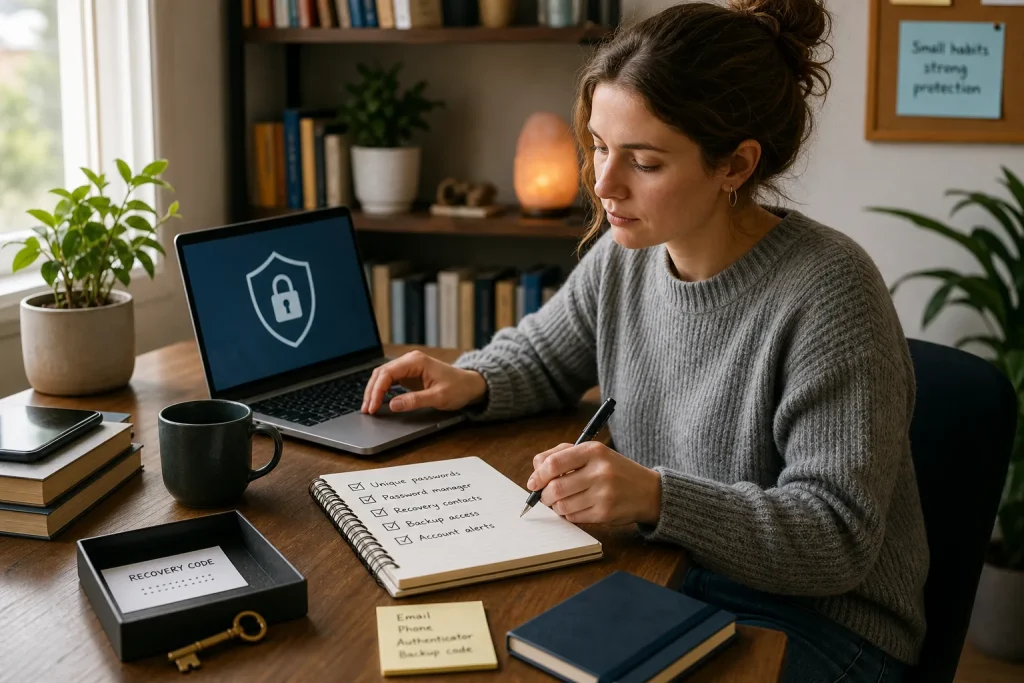
Password security can feel like an all-or-nothing project: change every login, memorize every new phrase, and never make a mistake. That expectation is difficult to sustain. A more practical routine gives each task a clear role. Unique passwords limit the reach of a compromised account, a password manager keeps those passwords usable, and recovery details help you regain access if you lose your usual sign-in method.
The aim is not to create a complicated ritual. It is to make secure choices the easy ones, then revisit the parts that can quietly become outdated. Common mistakes are ordinary: reusing a familiar password, keeping the only recovery code in the account it unlocks, or postponing manager setup until an urgent sign-in problem appears. A focused decision checklist turns these risks into manageable choices.
Give each account a distinct password
Reusing a password is tempting because it makes familiar websites easy to enter. But a password should not serve as a master key across unrelated accounts. If one service is breached, a reused credential may expose other accounts that accept the same combination. Give particular attention to email, financial services, cloud storage, and accounts that can reset passwords elsewhere. Those accounts often provide routes into other parts of your digital life.
Unique does not have to mean memorable. A password manager can create and store a different strong password for each account, so you do not need to invent a memorable variation each time. Avoid predictable changes such as adding a number to an old password. If a service offers passkeys or another sign-in method, consider its recovery and device requirements before switching. Choose a method you can use and recover safely.
Choose a manager you can actually use
A password manager is useful only if it fits the devices and sign-in habits you rely on. Consider whether it works with your phone and computer, whether its recovery options make sense to you, and whether its autofill behavior lets you check that you are on the right website before entering credentials. A built-in manager may suit someone who uses one platform consistently; a dedicated manager may fit someone who moves among different devices. Neither choice removes the need to protect access to the manager itself.
Start by setting up the manager and learning how to retrieve a saved login before moving every account. Protect its primary account with a distinctive password and any additional sign-in safeguard it offers. Learn what happens if you forget that password or lose a trusted device. Do not assume the provider can restore access in every situation. The manager’s recovery process is part of your routine, not a detail to discover during an emergency.
Avoid common setup mistakes
Trying to update every login in one sitting can lead to rushed choices, missed accounts, and half-finished changes. Changing passwords on a shared or untrusted device can also leave credentials accessible to someone else. Use a device you control and work through accounts in a sensible order. Begin with the email account that handles password resets, then move to accounts that hold sensitive information or control access to other services.
Storing a password does not, by itself, secure an account. A manager cannot correct an outdated recovery email, and a unique password may not prevent someone from approving a deceptive sign-in request. Keep device software current, use additional authentication where it is available and appropriate, and treat unexpected login prompts cautiously. If a service reports a compromise, consult that service’s official account-security instructions for the specific incident. Follow its directions for affected accounts and related actions rather than assuming every account needs the same response.
Keep recovery details separate and current
Recovery details are routes back into an account: a backup email address, phone number, trusted device, authenticator method, or recovery code. Check that you can still access the listed email and phone, especially after changing providers or devices. Store recovery codes somewhere you can reach if your main device is unavailable, but not in the same account they are meant to recover. Choose a secure, practical location and know how you would find it.
Consider the balance between convenience and resilience. A recovery method that is easy to reach may be unavailable if it depends on a device you lose. A method that is extremely secure but impossible to locate is not a workable backup. Follow each service’s instructions, avoid sharing recovery codes, and remove old phone numbers or devices when you no longer control them. If an account is tied to work, family care, or an essential service, ask the relevant provider or administrator about its supported recovery process.
Use a decision checklist for routine upkeep
Rather than changing every password on a recurring schedule, check whether anything meaningful has changed. Focus on account access, recovery routes, and signs of reuse. If a service reports a breach, a device is lost, or someone else may know a password, address the affected account promptly. If that password was reused, consider the other accounts where it appears as well. For a reported incident, let the service’s current guidance shape the response; do not treat a general routine as a substitute for incident-specific directions.
- Password reuse: Check whether the same password appears on another account. If it does, replace it with a unique credential on the affected accounts; if it does not, leave it unchanged unless another concern applies.
- Manager access: Check whether you can sign in on your usual devices and identify the official recovery route. If either is unclear, resolve that issue before migrating more accounts; if both are clear, continue using the manager.
- Recovery contacts: Check whether the listed email address and phone number are still under your control. If either is outdated, update it through the service’s account settings; if both are current, keep them in place.
- Backup access: Check whether you could retrieve a recovery code without your primary device. If not, store a newly issued code in a separate secure location; if you can, retain it there and avoid making unnecessary copies.
- Account alerts: Check whether a sign-in alert or service notice is unfamiliar. If it is, use the service’s official security guidance and secure the affected account; if it is familiar, do not change credentials solely because the alert appeared.
- Device changes: Check whether a trusted phone or computer is being retired. If it is, add and verify its replacement using each service’s instructions before removing the old device; if no device is changing, leave trusted-device settings alone.
Work through a phone transition carefully
Consider this invented hypothetical situation: a person is replacing a phone that contains an authenticator app, while their email account serves as the recovery address for several services. They still have access to the old phone, want to avoid losing access, and have no reason to change every password. Their starting decision is to keep the old phone available until the new sign-in and recovery arrangements are confirmed. This preserves a current route into accounts while they handle the transition.
They first sign in to the password manager on the new phone and check that saved logins are available. Next, they open each important service and follow its instructions to add the new authenticator or trusted device, then confirm that the recovery email remains accessible. They save any newly issued recovery codes separately from the accounts they protect. Finally, they verify the new sign-in route and remove the old phone from account settings. The expected result is continued access with a fallback in place; the tradeoff is spending focused time on important accounts before retiring the old device.
A sustainable password routine has a clear purpose at every stage: distinct credentials reduce the consequences of reuse, a manager makes those credentials manageable, and current recovery details provide a route back in. Keep the routine focused on meaningful changes rather than constant maintenance. When you add an account, secure it with a unique credential and usable recovery options. When a device or contact method changes, update the accounts that depend on it. Small, deliberate decisions make good habits easier to keep.